

M2P Fintech
Fintech is evolving every day. That's why you need our newsletter! Get the latest fintech news, views, insights, directly to your inbox every fortnight for FREE!

Welcome to our latest blog, where we dive into the critical security technique known as SSL Pinning. This method plays a pivotal role in thwarting eavesdropping attacks on the communication between an app and its server.
SSL Pinning involves a process where, after the initial exchange of encryption keys, the app verifies the validity of the server's certificate. It achieves this by maintaining a list of trusted certificates on the device itself, which are then compared to the server's certificate in real time as the app operates.
If there is a discrepancy, indicating that the server's certificate does not align with the trusted ones, the app promptly halts the connection.
Types of SSL Pinning:
Mobile applications must retrieve data from the server to display it to consumers. However, private data, such as the user's login and password, is occasionally transmitted between the program and the server. SSL Pinning is mainly used in the prevention of man-in-the-middle attacks.
Man-In-The-Middle Attack
This type of attack allows the attacker to covertly view data passed from the client to the server by using a specialized server called an SSL proxy. It is a tool that encrypts and decrypts data between the client and the server using different keys for each direction. Charles, a proxy server used for testing, is one such example. It works in several phases to intercept and analyze the data between the app and the server. By sitting between the app and the internet, it allows you to examine and modify data in real-time to test the response of the application.
SSL Pinning using Public Key
echo "Get HTTP/1.0" | openssl s_client -showcerts -connect
www.MyDomainName.com:443 > myPemCertificateName.pem
openssl x509 -in "myPemFileName.pem" -inform PEM -out "myDerFileName.der" -outform DER
openssl s_client -connect www.MyDomainName.com:443 | openssl x509 -pubkey -noout | openssl rsa -pubin -outform der | openssl dgst -sha256 -binary | openssl enc -base64
A3r26k+KOMuKJHB5B67cpGqqPhF/GNUyNl2EPJKB65KJUe+hXMn1k=
static let sslPublicKey =
"A3r26k+KOMuKJHB5B67cpGqqPhF/GNUyN2EPJKB6KJUe+hXMn1k="
Pinning with Alamofire
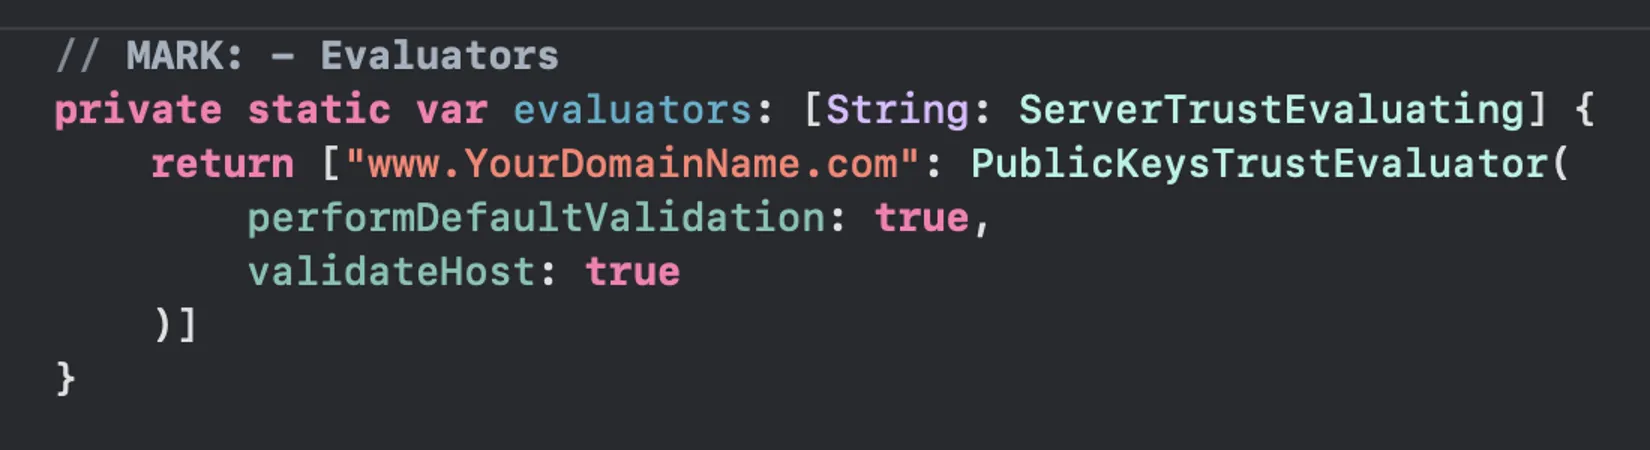
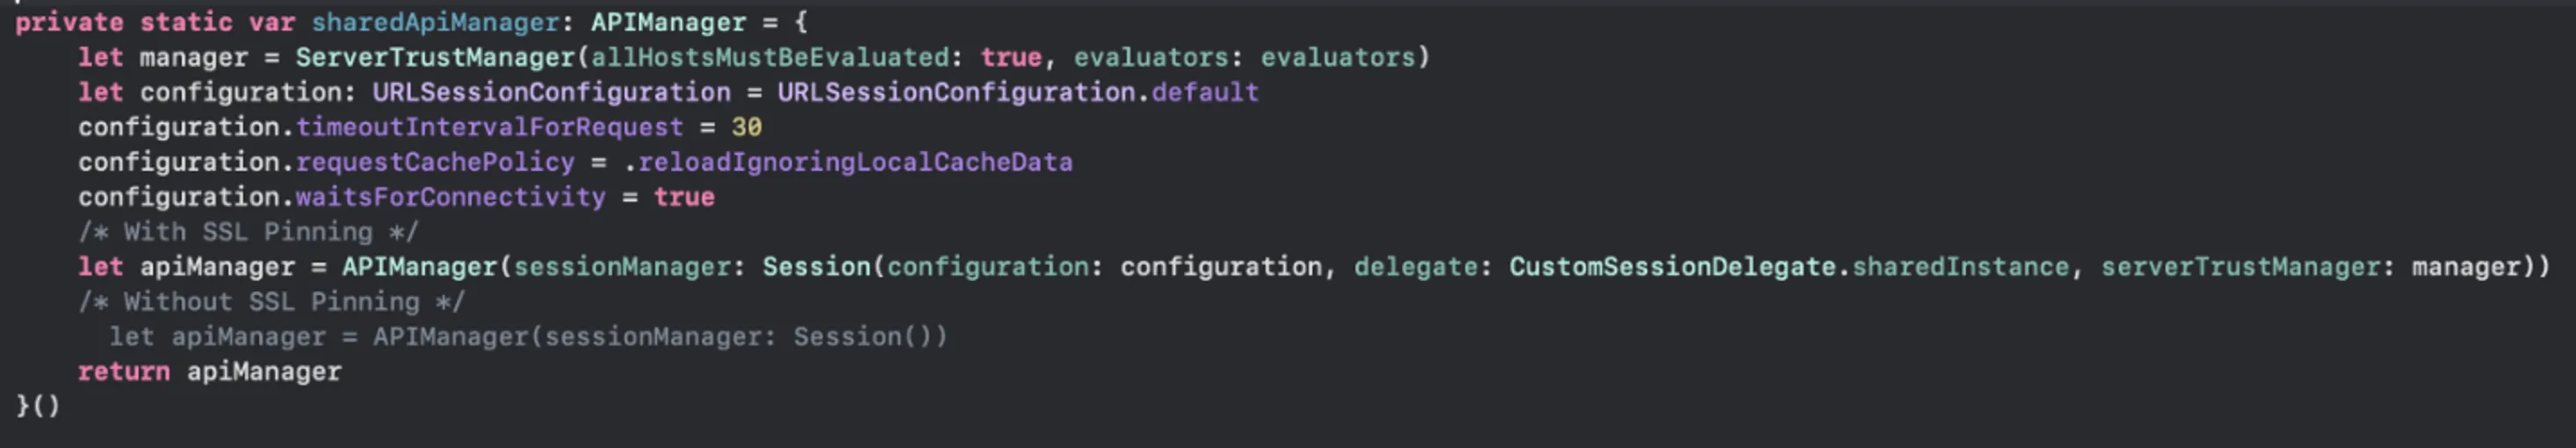

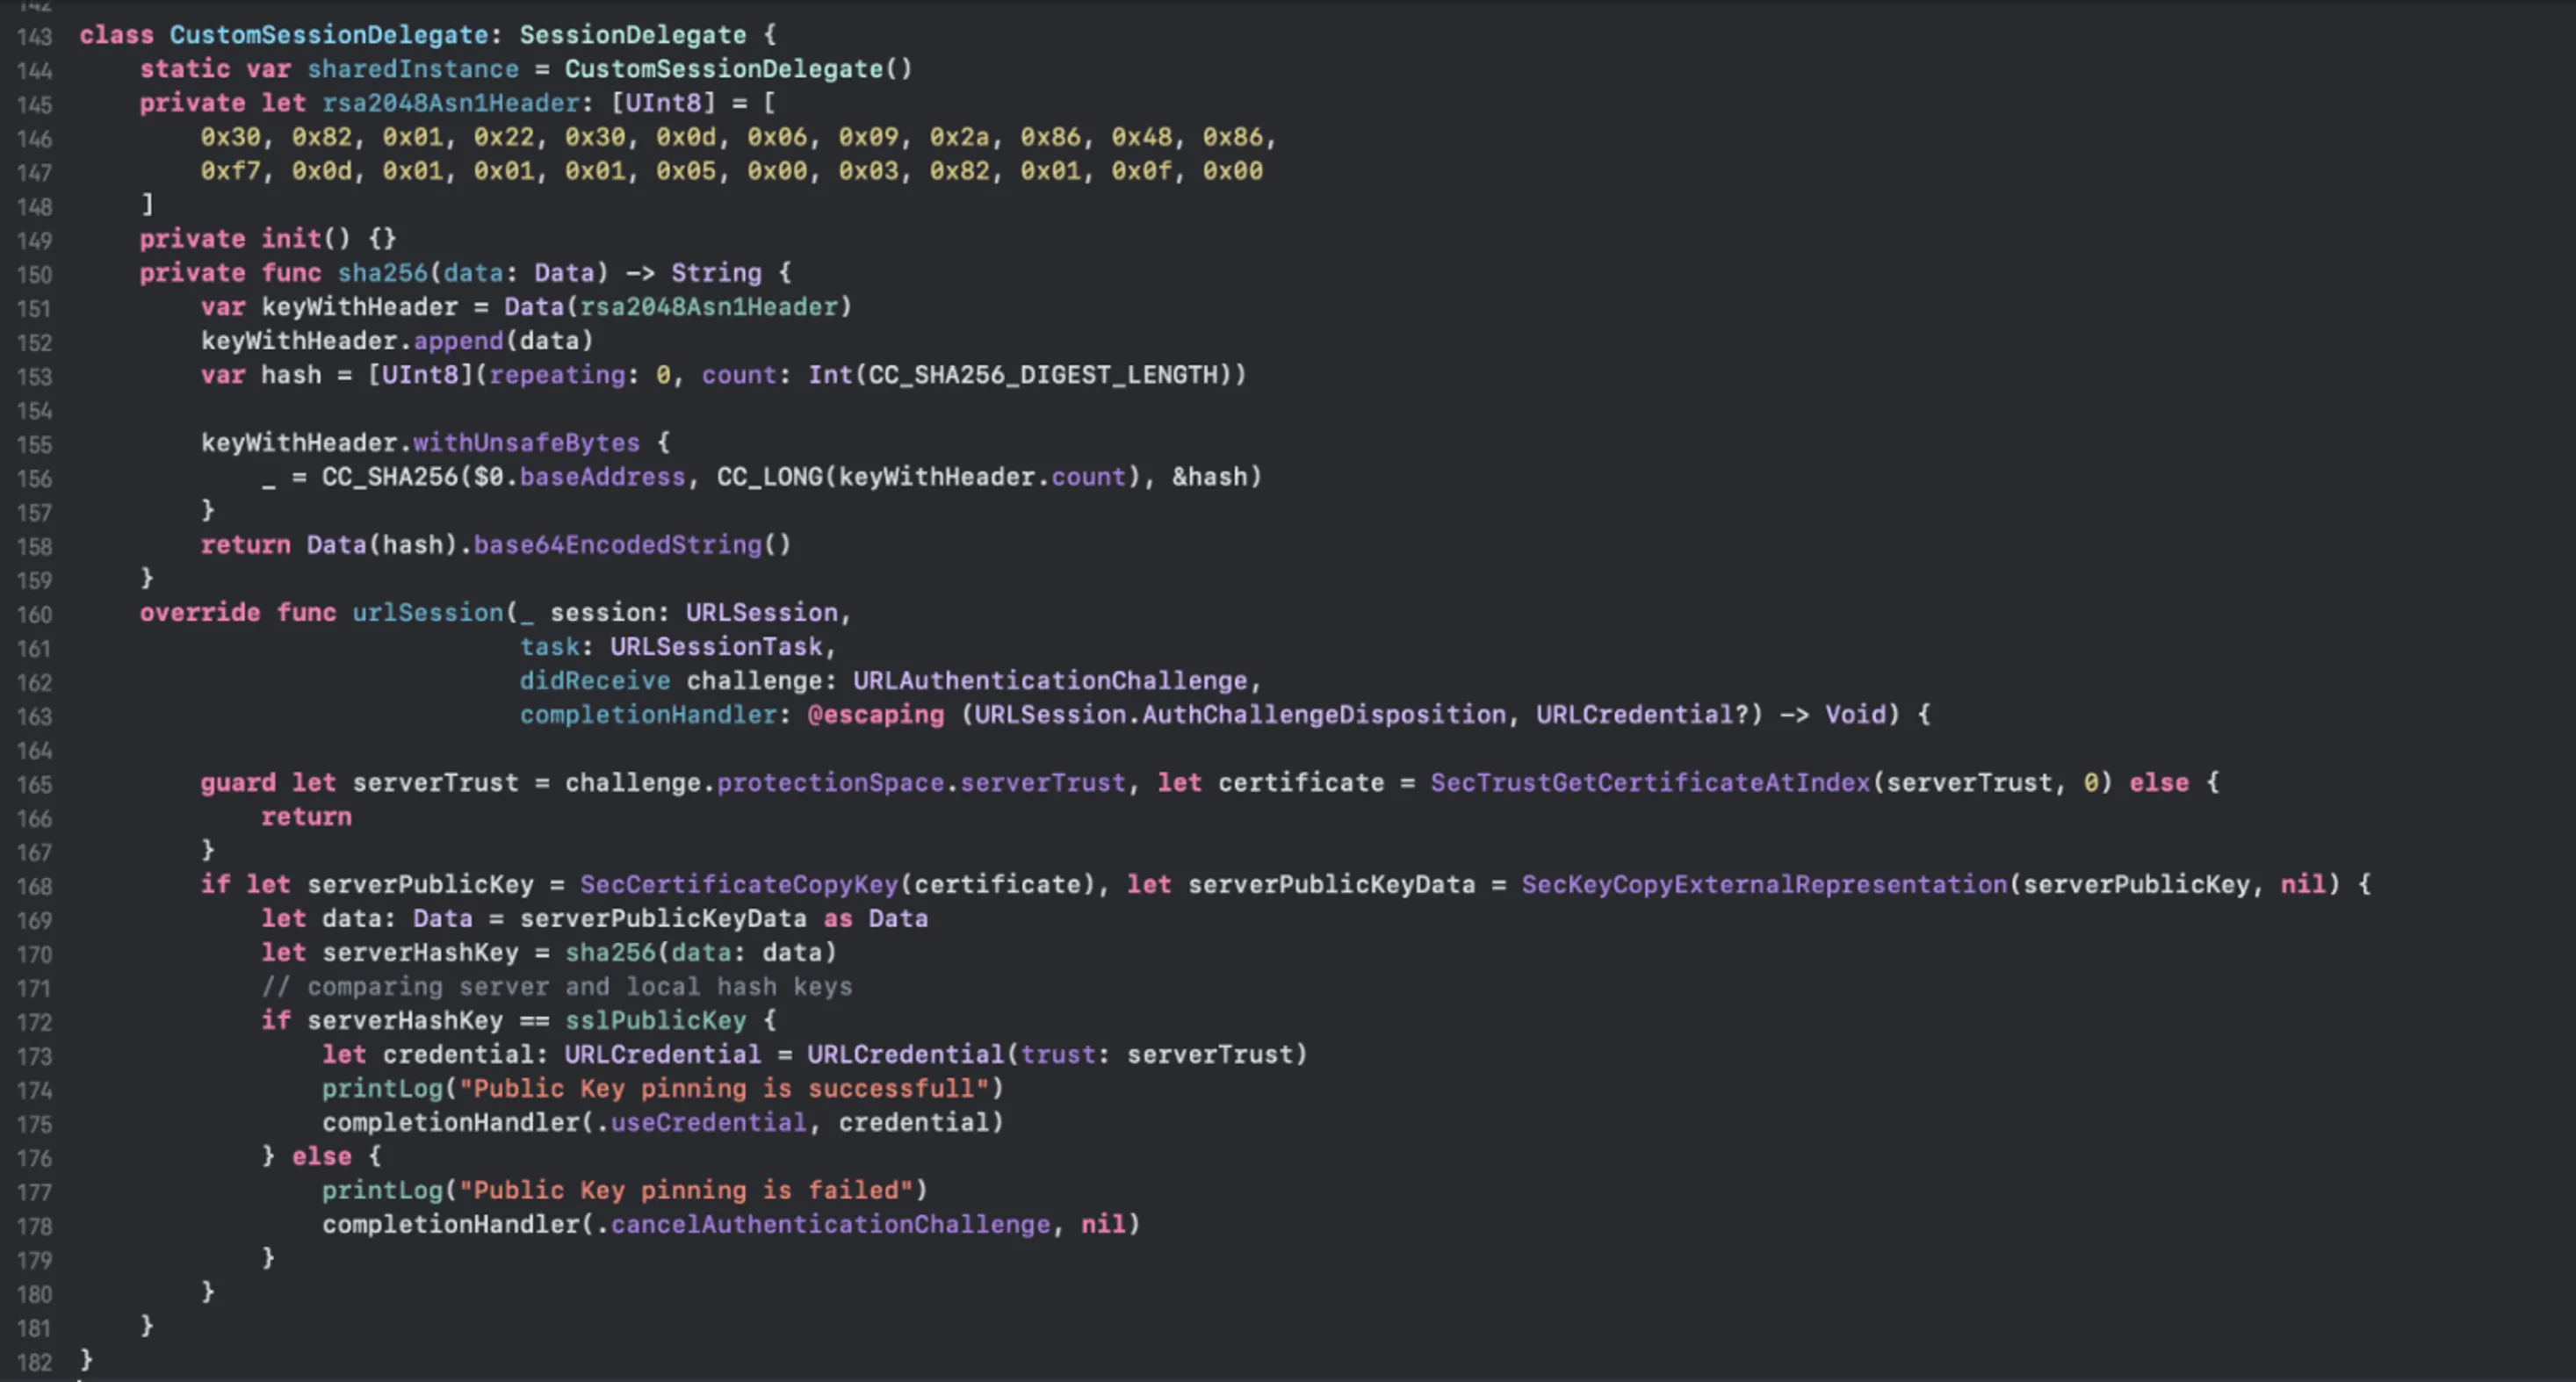
Implementing SSL pinning using a public key in iOS enhances security by ensuring that only trusted servers with specific public keys can establish connections. This method mitigates the risks associated with man-in-the-middle attacks and unauthorized access to sensitive data, providing users with a more secure experience.
Stay tuned for more blogs on tech, engineering, and iOS development.
This blog is written by Senthilkumar, SDE 2 – Product Engineering at M2P.


Fintech is evolving every day. That's why you need our newsletter! Get the latest fintech news, views, insights, directly to your inbox every fortnight for FREE!